Jekyll2026-10-02T05:33:31+00:00https://nirajankunwor.com.np/feed.xmlblankNirajan Kunwor — Senior Software Engineer. Research interests in machine learning, medical AI, computer vision, domain generalization, test-time adaptation, federated learning. Secure File Transfer: A Beginner’s Guide to Uploading and Downloading Files with SCP2024-11-22T04:11:33+00:002024-11-22T04:11:33+00:00https://nirajankunwor.com.np/blog/2024/secure-file-transfer-a-beginners-guide-to-uploading-and-downloading-files-with-scpTransferring files securely between a local machine and a remote server is a common task for developers, system administrators, and anyone managing servers. One of the most secure and efficient ways to achieve this is by using SCP (Secure Copy Protocol). In this blog, I’ll walk you through the process of uploading and downloading files with SCP, using an example command for each case.
What is SCP?
SCP is a command-line tool that allows you to transfer files between your local machine and a remote server over an encrypted SSH connection. This ensures your files remain secure during the transfer process. It’s simple, fast, and widely used in the tech world.
1. Uploading Files to the Server
Let’s say you want to upload a file named backend.zip from your local machine to a remote server’s /home/ubuntu/ directory.
-i abc.pem: Specifies the private key file for authentication.
backend.zip: The file on your local machine that you want to upload.
ubuntu@10.10.10.10: The username (ubuntu) and the server’s IP address (10.10.10.10).
/home/ubuntu/: The destination directory on the server.
2. Downloading Files from the Server
To download the backend.zip file from the remote server’s /home/ubuntu/ directory to your local machine’s ~/Downloads folder, use the following command:
-i abc.pem: Specifies the private key file for authentication.
ubuntu@10.10.10.10:/home/ubuntu/backend.zip: The file’s path on the remote server.
~/Downloads/: The destination folder on your local machine.
Key Points to Remember
Use Absolute Paths for Clarity: Always use full paths for both local and remote locations to avoid confusion.
File Permissions: Ensure you have the correct permissions for the directory where the file is being uploaded or downloaded.
Security Matters: Keep your private key (abc.pem) secure and do not share it with anyone.
Conclusion
Using SCP for secure file transfer is an essential skill for anyone working with remote servers. Whether you’re deploying a project or backing up important files, SCP provides a secure and straightforward way to move your data.
In Plain English 🚀
Thank you for being a part of the In Plain English community! Before you go:
]]>5 Essential Node.js Security Best Practices to Keep Your Application Safe2024-11-06T05:25:35+00:002024-11-06T05:25:35+00:00https://nirajankunwor.com.np/blog/2024/5-essential-nodejs-security-best-practices-to-keep-your-application-safe
Rate Limiting: Rate limiting and throttling are essential techniques to protect applications from abuse, such as brute-force attacks, denial-of-service (DoS) attacks, and resource exhaustion. They help ensure that your application can handle genuine traffic without being overwhelmed by excessive requests from single or multiple sources.
Using express-rate-limit in Node.js: express-rate-limit is a middleware package for Express applications that provides a straightforward way to set rate limits on your API endpoints.
// Define rate limit
const limiter = rateLimit({
  windowMs: 15 * 60 * 1000, // 15 minutes
  max: 100, // limit each IP to 100 requests per windowMs
  message: "Too many requests from this IP, please try again later.",
});

// Apply the rate limit to all requests
app.use(limiter);
It’s not ideal for handling high volumes of traffic, as the rate limiting logic is processed by the Node.js server itself, which can still be vulnerable to high traffic.
Using Rate Limiting at the Nginx Server Level: Nginx is designed to handle a high number of requests efficiently, and performing rate limiting directly at the web server level reduces the load on the application server (Node.js). This keeps your backend resources focused on serving legitimate requests.
http { # Define a limit request zone limit_req_zone $binary_remote_addr zone=api_limit:10m rate=10r/s;
limit_req_zone $binary_remote_addr zone=api_limit:10m rate=10r/s;: This directive defines a zone named api_limit that allows up to 10 requests per second per IP address. $binary_remote_addr tracks IP addresses in a compact, binary format.
burst=20: Allows up to 20 requests to exceed the rate limit in short bursts.
nodelay: Sends the requests immediately if there’s available burst capacity.
2. JWT Blacklisting:
JWTs cannot be invalidated by default because they are stateless. This means:
If a token is compromised or if a user logs out, there’s no built-in way to invalidate the token.
Until the token expires, the holder of the token can access the application’s resources.
To overcome this, we use JWT blacklisting. Blacklisting is especially important for refresh tokens, as they are long-lived and allow users to get new access tokens.
Using a Rotating Refresh Token Strategy
Generate and Rotate Refresh Tokens:
When a user requests a new access token, generate a new refresh token and save it in the database or Redis with a reference to the user. Invalidate the old refresh token by removing it from the database.
async function refreshTokens(oldRefreshToken) {
  const decoded = verifyRefreshToken(oldRefreshToken);

  // Check if the token is still valid in the database
  const storedToken = await db.getRefreshToken(decoded.jti);
  if (!storedToken) return res.status(401).send("Invalid refresh token");

  // Generate a new refresh token and invalidate the old one
  const newRefreshToken = generateRefreshToken(decoded.userId);
  await db.saveRefreshToken(newRefreshToken);
  await db.deleteRefreshToken(decoded.jti);

  return newRefreshToken;
}
Store Only the Latest Refresh Token:
Only one valid refresh token exists at any given time for a user. If a user tries to use an old refresh token, it will no longer be in the database or cache, so it will be rejected.
3. Preventing XSS in Node.js Applications
Sanitize and Validate User Inputs
XSS vulnerabilities often arise when user-provided data is rendered on the page without proper sanitization. For instance, if users can submit comments or messages, an attacker might inject malicious JavaScript code that would execute on another user’s browser.
Use input validation libraries like express-validator or Joi to ensure inputs meet specific formats and strip out potentially dangerous characters.
app.post('/submit-comment', [ body('comment').isString().trim().escape(), // Sanitize input ], (req, res) => { const errors = validationResult(req); if (!errors.isEmpty()) { return res.status(400).json({ errors: errors.array() }); } // Process comment here });
Escape Output Properly
If you’re rendering HTML on the server-side (e.g., using template engines like EJS, Pug, or Handlebars), ensure all data that comes from user input is properly escaped. Most modern templating engines handle this by default, but it’s good practice to double-check.
Escaping converts special characters (<, >, &, ", ') to HTML entities so they’re displayed as text rather than interpreted as HTML or JavaScript.
Cookies are often used to store session IDs, so it’s important to configure them securely:
Secure Flag: Set the Secure flag on cookies so they are only sent over HTTPS connections.
HttpOnly Flag: Set the HttpOnly flag to prevent JavaScript access to cookies, which helps protect against XSS attacks.
SameSite Attribute: Set SameSite to Strict or Lax to restrict cross-site request behavior, reducing the risk of CSRF (Cross-Site Request Forgery) attacks.
const session = require('express-session');
// Generating a secret using Node's crypto module
const crypto = require('crypto');
const sessionSecret = crypto.randomBytes(64).toString('hex');

app.use(session({
  secret: sessionSecret,
  resave: false,
  saveUninitialized: true,
  cookie: {
    httpOnly: true,      // Prevents JavaScript access to cookies
    secure: true,        // Ensures cookies are only sent over HTTPS (useful in production)
    sameSite: 'lax'      // Mitigates CSRF attacks by restricting cross-site requests
  }
}));
Use Short Session Expiration and Automatic Session Renewal
Sessions that last too long increase the risk of session hijacking if an attacker gains access to a session token. Implementing session expiration and automatic renewal minimizes this risk.
Short Expiry Times: Set short expiration times for session cookies, depending on your application’s needs. For example, a session timeout of 15–30 minutes of inactivity is common.
Automatic Renewal: Renew session expiration on each interaction to keep active users logged in but expire inactive sessions automatically.
// Middleware to renew session expiration on each request app.use((req, res, next) => { if (req.session) { req.session._garbage = Date(); req.session.touch(); } next(); });
5. Prevent HTTP parameter pollution
To prevent HTTP Parameter Pollution, you can use the hpp middleware in your Node.js application. The hpp library (short for HTTP Parameter Pollution) is a simple, effective tool for handling duplicate parameters. It ensures that only the first occurrence of a parameter is accepted, discarding duplicates and eliminating potential issues.
app.get('/search', (req, res) => { // Only the first instance of each query parameter is used console.log(req.query); // { category: 'electronics' } res.send('Search results'); });
app.listen(3000, () => { console.log('Server running on port 3000'); });
In this example, if a request like https://example.com/search?category=electronics&category=clothing is made, the hpp middleware will ensure only the first category parameter is considered (electronics), and the duplicate is ignored.
Securing a Node.js application requires a proactive approach across various layers of your stack. By implementing best practices like rate limiting, JWT blacklisting, secure session management, and protections against XSS and HTTP parameter pollution, you can greatly reduce the risk of common vulnerabilities. Prioritizing security not only protects your data but strengthens the overall resilience of your application.
In Plain English 🚀
Thank you for being a part of the In Plain English community! Before you go:
]]>Migrating Your Existing Node.js App to AWS Lightsail: A Practical Guide2024-07-15T15:42:57+00:002024-07-15T15:42:57+00:00https://nirajankunwor.com.np/blog/2024/migrating-your-existing-nodejs-app-to-aws-lightsail-a-practical-guideINTRODUCTION
Amazon Lightsail offers a simplified way to deploy and manage applications in the cloud. In this guide, we’ll walk through the process of hosting a Node.js application on an AWS Lightsail instance, taking advantage of its user-friendly interface and seamless integration with AWS services.
PREREQUISITES
Basic knowledge of Node.js and npm
An AWS Account
Familiarity with Linux command line
Your existing Node.js application code
Preparing for Migration
a. Choose a Lightsail plan:
Login to the AWS console and search or Navigate to the Light Sail console below shown image and click on the create instance for creating a server.
Next you have to choose the Image you want for your server since most of the nodejs applications runs based on the Ubuntu server. I choose choose the OS only option and manually configure all needs, then scroll down for next.
Select a pricing model that suits your applications need.
Add your instance name and click create instance as shown on the picture below.
Once created, you can see the instance spinning up and ready in a while.
b. Configuring Lightsail:
Click on the instance and you will then move into the detailed view of the instance. Click on the networking tab.
On networking, add the port as custom which is used in your nodejs application like 3000 or 5000 as seen in the image below. Used for Secure Shell (SSH) connections
Port 22 (SSH): Used for Secure Shell (SSH) connections
Port 80 (HTTP): Used for standard web traffic
Port 443 (HTTPS): Used for secure web traffic
Port 5000 (Custom): This is a custom nodejs application port
Port 5000 (Custom): Another custom application port
C. Deploying your Node.js Application
Open ssh and move to root. Run following commands.
Clone the project in any location on home or create a new folder. Install pm2 process manager and start the project.
D. Reverse proxy setup:
If your Node.js application operates on a non-standard port (such as 3000 or 5000), consider setting up a reverse proxy using Nginx or another server. This will forward requests to your Node.js application, bolstering security and enabling the use of a custom domain.
sudo apt install nginx

sudo systemctl start nginx

sudo systemctl enable nginx
Place your project files in /var/www/html/
Edit the default configuration file at /etc/nginx/sites-available/default
If you are using a custom domain name, go to your dns provider and add A record
E. Setup SSL/TLS
Finally, the only task left to do here is to secure our web server with SSL encryption. We can do this with the Certbot library very easily.
Install Certbot and prepare certbot command.
sudo snap install --classic certbot
sudo ln -s /snap/bin/certbot /usr/bin/certbot
Run this command to get a certificate and have Certbot edit your nginx configuration automatically to serve it, turning on HTTPS access in a single step.
sudo certbot - nginx
Test automatic renewal
sudo certbot renew --dry-run
To confirm that your site is set up properly, visit https://yourwebsite.com/ in your browser and look for the lock icon in the URL bar.
That’s it. Now you have a secure web application running in your AWS Lightsail Instance. 👏
Conclusion: AWS Lightsail streamlines Node.js application hosting, combining the power of AWS infrastructure with a user-friendly interface. This approach lets developers focus on crafting exceptional applications rather than grappling with complex server management. By following a straightforward deployment process, you can effortlessly launch, maintain, and expand your Node.js projects, freeing up valuable time and resources for innovation and feature development.
In Plain English 🚀
Thank you for being a part of the In Plain English community! Before you go:
]]>SOLID principles made easy — JavaScript & TypeScript2022-11-25T11:32:10+00:002022-11-25T11:32:10+00:00https://nirajankunwor.com.np/blog/2022/solid-principles-made-easy--javascript--typescriptThe SOLID Principles are five principles of Object-Oriented class design. They are a set of rules and best practices to follow while designing a class structure.
So, what is SOLID? How does it help us write better code? Simply put, these principles encourage us to create more maintainable, understandable and clean code.
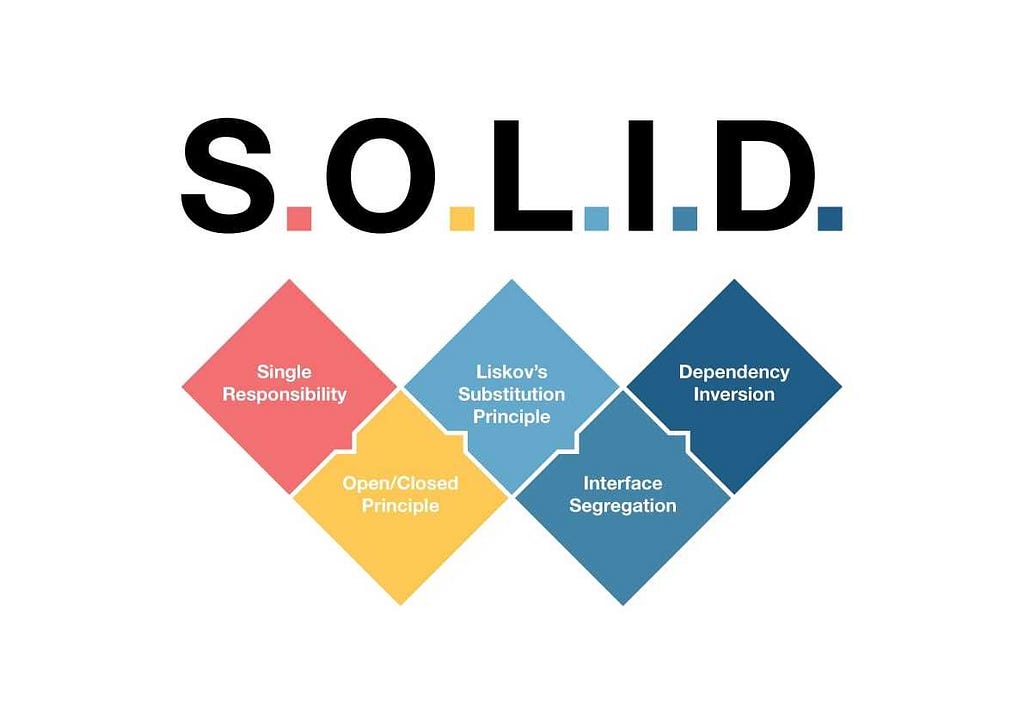
Following the SOLID acronym, they are:
[S] Single Responsibility Principle
There should never be more than one reason for a class to change. In other words, every class should have only one responsibility.
[O] Open–Closed Principle
Software entities like classes, functions, etc should be open for extension, but closed for modification.
[L] Liskov Substitution Principle
Subclasses should be substitutable for their base classes.
[I] Interface Segregation Principle
This principle states that many client-specific interfaces are better than one general-purpose interface. Clients should not be forced to implement a function they do no need.
[D] Dependency Inversion Principle
High level modules should not depend on low level modules; both should depend on abstractions.
Let’s learn about these principles in detail with some examples in Javascript and Typescript.
# Single Responsibility Principle
The single responsibility principle states that every module, class or function in a computer program should have responsibility over a single part of program’s functionality.
If a class has many responsibilities, it increases the possibility of bugs as making change to any of the functionality may affect others without knowing.
Advantages
Clean and standard code
Manageable and easy for maintenance
Easy to refactor or change
Readable code
Disadvantages
To many small modules/classes
Take more time for development and increases project cost
Example
Let’s take a look at the following code:
class TodoList { constructor() { this.items = [] }
Thus our code has become more scalable. Of course, it may not look feasible when we look at small solutions. When applied to a complex architecture, this principle makes more meaning.
# Open Closed Principle
Objects or entities should be open for extension, but closed for modification.
Open for extension means that we should be able to add new features or components to the application without breaking existing code. Closed for modification means that we should not introduce breaking changes to existing functionality, because that would force us to refactor a lot of existing code.
Changing the current behaviour of a class will affect all the systems using that class. If we want the class to perform more functions, the ideal approach is to add to the functions that already exist not change them.
Advantages
Extensibility
Maintainability
Flexibility
Disadvantages
The resource allocator code needs to be unit tested whenever a new resource type is added
Adding a new resource type introduces considerable risk in the design as almost all aspects of resource allocation have to be modified
Developer adding a new resource type has to understand the inner workings for the resource allocator
Example
Let’s take a look at the following code:
class Person{ constructor(fullName, language, hobby, education, workplace, position) { this.fullName = fullName this.language = language this.hobby = hobby this.education = education this.workplace = workplace this.position = position } }
The problem with PersonFilter is that if we want to filter by any other new property we have to change PersonFilter’s code. Let's solve this problem by creating a filterByProp function which will filter by the properties.
class Person{ constructor(fullName, language, hobby, education, workplace, position) { this.fullName = fullName this.language = language this.hobby = hobby this.education = education this.workplace = workplace this.position = position } }
If S is a subtype of T, then objects of type T in a program may be replaced with objects of type S without altering any of the desirable properties of that program.
When a child Class cannot perform the same actions as its parent Class, this can cause bugs.
If you have a Class and create another Class from it, it becomes a parent and the new Class becomes a child. The child Class should be able to do everything the parent Class can do. This process is called Inheritance.
Advantages
It ensures correct sub-hierarchy with relevant checks
It becomes easy to extend new classes
The maintainability of code becomes very easy
There shall be no runtime surprises in the application
Disadvantages
Sometimes we need to update base class in order to support new extension
You may need to refactor a lot of things
Cost of refactor
Example
Let’s take a look at the following code:
class Bird {
    fly(){
        //..
    }
}

class Eagle extends Bird {
    dive(){
        //..
    }
}

const eagle = new Eagle();
eagle.fly();
eagle.dive();

class Penguin extends Bird(){
   //Problem: Can't fly!
}
The problem is that Penguin can’t fly. So to solve this problem, we have to create separate class for different kind of birds. Let’s look at the following example to solve above problem.
class Bird {
  layEgg () {}
}

class FlyingBird {
  fly () {}
}

class SwimmingBird extends Bird {
  swim () {}
}

class Eagle extends FlyingBird {}

class Penguin extends SwimmingBird {}

const penguin = new Penguin();
penguin.swim();
penguin.layEgg();

const eagle = new Eagle();
eagle.fly();
eagle.layEgg();
# Interface Segregation Principle
Clients should not be forced to depend upon interfaces that they do not use.
When a Class is required to perform actions that are not useful, it is wasteful and may produce unexpected bugs if the Class does not have the ability to perform those actions.
A Class should perform only actions that are needed to fulfil its role. Any other action should be removed completely or moved somewhere else if it might be used by another Class in the future.
Advantages
Faster Compilation
Reusability
Maintainability
Easier to understand
Lighter to test
Quicker to change
Disadvantages
You may need to refactor a lot of things
Cost of refactor
Example
Let’s take a look at the following code:
In the following example we have an interface for animals with 2 methods: walk and fly.
As you can see, the Dog class has to implement the method fly even though that class does not need it.
interface Animal {
  walk(): void;
  fly(): void;
}

class Dog implements Animal {
  walk() {
    console.log("Walking");
  }

  fly() {
    throw new Error("Dogs cannot fly");
  }
}

class Duck implements Animal {
  walk() {
    console.log("Walking");
  }

  fly() {
    console.log("Flying");
  }
}
Following this principle we can split the Animal interface into multiple ones. This way, the Dog class will only have to implement the methods that it needs.
interface AnimalCanWalk {
  walk(): void;
}

interface AnimalCanFly {
  fly(): void;
}

class Dog implements AnimalCanWalk {
  walk() {
    console.log("Walking");
  }
}

class Duck implements AnimalCanWalk, AnimalCanFly {
  walk() {
    console.log("Walking");
  }

  fly() {
    console.log("Flying");
  }
}
# Dependency Inversion Principle
High-level modules should not depend on low-level modules. Both should depend on the abstraction.
In plain terms, this principle states that your classes should depend upon interfaces or abstract classes instead of concrete classes and functions. This makes your classes open to extension, following the open-closed principle.
Advantages
Your code will not be coupled to external API or other implementations
Scalable
Maintainable
Clean
Disadvantages
You may need to refactor a lot of things
Cost of refactor
Example
Let’s take a look at the following code:
In the following bad example we have the OrderService class that saves orders in a database. The OrderService class depends directly on the low level class MySQL database.
If in the future we wanted to change the database that we are using we would have to modify the OrderService class.
class MySQLDatabase { insert(order: Order) { // insert }
update(order: Order) { // update } }
We can improve this by creating an interface and make the OrderService class dependant of it. This way, we are inverting the dependency. Now the high level class depends on an abstraction instead of a low level class.
Now we can add new databases without modifying the OrderService class.
Summary
So far, we have discussed five principles with examples in Javascript and Typescript. When you design your architecture, If you ask yourself “Am I violating SOLID principles” , I promise that the quality and scalability of your code will be much better.
Thank you so much for reading. I hope you have a better idea about this topic and you had as much fun reading this as I did writing it.
If you have any questions or suggestions, leave a comment.
In Plain English 🚀
Thank you for being a part of the In Plain English community! Before you go:
]]>Digitalization in Nepal2021-06-09T12:30:03+00:002021-06-09T12:30:03+00:00https://nirajankunwor.com.np/blog/2021/digitalization-in-nepal
Sixty-two years after the erstwhile Soviet Union launched Sputnik-1, the world’s first satellite, Nepal sent its first satellite ‘NepaliSat-1’ into space in April 18 to at around 2:31 am. A landlocked country, bordering Tibet of China to the north, and India in the south, east, and west, my country is counted as one of the developing countries of the world . While I was studying in college, I used to watch science fiction movie such as advanced science and technology, space exploration, time travel, and then think how fast the technologies had grown. I used to think ‘Can my country within the Himalayas be so advanced in technologies and digitalization?’. But today I see that we are slowly coming across the dream of digitalization. I realize today that ‘ Rome was not built in a day’ and then we must all contribute to bring the change we wish to see. 2020 brought along a new outlook to this country and a different understanding towards a great deal of things; Digitalization being one of them.
The pandemic changed the people’s perspective towards digital payment in Nepal. Although digital payment services had slowly been proceeding towards tentative growth with the innovation in technology, the industry was yet to reach higher ground compared to other countries . We are now quickly adapting and undertaking the usage of digital payment services for our daily expenses and micro payments. Digital payment methods took speed as a way for people as the lockdown was implemented when the Covid-19 virus first hit Nepal; by now people have become more familiar, discovering saved time, lower costs and better client experience. But there’s more trust to be build around these online services as we listen some fraudulent activities. Digitalization also reduced the virus transmissibility through cross contamination.
There is a growing level of easiness among local businesses in receiving customer payments contactless and digitally from various payment getaways. Nepalese merchants have now come to the realization that, use of wallet payment services not only reduces the overall transaction cost but also offers customers better security for their payments made, while customers furthermore come to trust their business . Digitalization also allows businesses to gain useful information about their customers and take a customer-centric approach to improve their services. Now, companies are actively participating and supporting digital payment service providers in educating the public on digitized payments, which is another big reason for the swift growth in the industry. Simultaneously, several goverment bodies and banking institutions of Nepal are engaging in promotional activities to encourage cash alternatives like Digital Wallets, QR Code Payments, E-banking and M-banking services.
Digital wallet and online payment services play a vital role in this 21st century, as users can, within a few taps on their smartphone, transfer money without the limitations of geographical barriers. Digital wallets grant you the convenience of not having to take your wallet out, nor do you have to count your change, swipe cards or fill out any details before making a transaction. A few taps on your phone and you’re done. Also now the NRB has directed that we can make some international payments putting some restrictions and that start has boosted youths and helped them in making international payments.
As the Digital Nepal program estimates to deliver an impact worth 800 million Nepalese rupees ($7.23 million) by 2022, already its IT-enabled services and business process outsourcing sector has been liberalized to allow 100 percent foreign direct investments, while the telecommunication sector allows 80 percent FDI. But Nepal’s ICT infrastructure still remains a work-in-progress. Under the sub-pillar of Infrastructure such as mobile network coverage and bandwidth performance, the WEF’s Network Readiness Index reflected a declining trend for Nepal over the last five years. As Nepal continues to leverage cooperation with multiple countries and not solely relying on India to strengthen its technological capacities, its policymakers and business communities must start capitalizing on Nepal’s growing ICT facilities — forming linkages between its satellite, optic cables, and upcoming 5G networks can bring Nepal one step further to integrate with the global digital economy.
Wrap Up:
Although, 2020 was a difficult year for all of us in every aspect and with the next wave of covid-19 , 2021 is also not going as expected. but we must adapt everyday to a new way of life, because it is during the darkest moment that we must focus to see the light and the light is digitalization and digital payment in Nepal which might just bring a revolution in our country.
]]>The Best Programming Languages to learn in 20212021-06-08T03:23:07+00:002021-06-08T03:23:07+00:00https://nirajankunwor.com.np/blog/2021/the-best-programming-languages-to-learn-in-2021Coding languages are evolving faster than any other area. Technologies have grown so much and developed so fast that even the slowest programming languages have been faster due to advancement in technology. For a tech newbie striving to learn programming, there are few languages I can suggest. But it is always about passion so find out what your heart is keen to learn.
Top 3 Programming languages to learn
Java
Platform: Web, Mobile, Desktop
Annual Salary Projection: around $ 79000
Description: Java is a high-level, class-based, object oriented programming language that is designed to have as few implementation dependencies as possible. It is a general-purpose programming language intended to let application developer write once, run anywhere (WORA), meaning that compiled Java code can run on all platforms that support Java without the need for recompilation
Why Java?
The answer to this question comprises of multiple reasons like its popularity, ease-to-learn nature, helpful open source tools and libraries etc. Gaining expertise in Java ensures a secure career with fat paychecks and the power to create applications with real-world applications.
Python
Platform: Web, Desktop
Annual Salary Projection: Around $75,000
Description:Python is an interpreted, object-oriented, high-level programming language with dynamic semantics. Its high-level built in data structures, combined with dynamic typing and dynamic binding, make it very attractive for Rapid Application Development, as well as for use as a scripting or glue language to connect existing components together.
Why Python?
Python is easy to use, powerful, and versatile, making it a great choice for beginners and experts alike. Python’s readability makes it a great first programming language — it allows you to think like a programmer and not waste time with confusing syntax. But don’t think that because Python is easy to use it’s a wimpy language. Python is incredibly powerful — there’s a reason companies like Google, Dropbox, Spotify, and Netflix use it.
JavaScript
Platform: Web, Mobile, Desktop
Annual Salary Projection: around $81000
Description: JavaScript is a cross-platform, object-oriented scripting language used to make webpages interactive (e.g., having complex animations, clickable buttons, popup menus, etc.). There are also more advanced server side versions of JavaScript such as Node.js, which allow you to add more functionality to a website than downloading files (such as real time collaboration between multiple computers). Inside a host environment (for example, a web browser), JavaScript can be connected to the objects of its environment to provide programmatic control over them.
Why JavaScript?
Today, JavaScript is one of the most powerful languages on the planet because of its performance and omnipresence. Personally, I feel like JavaScript has the potential to tap into so many popular industries like Machine Learning and Data Analysis, where Python still rules the game. It’s even happening now with tools like Tensorflow.js! Of course, nothing really beats C/C++/Rust, but JavaScript is a fast — in the sense that V8 can generate highly optimized code by monitoring how your code executes, delaying the bits of execution which are not used, and optimizing the code segments which are used over and over. JavaScript (Node) is highly scalable (with supersets like TypeScript). Running on a single threaded architecture, people often criticize Node for its lack of threading environment, but the reality is it doesn’t matter a lot.
Wrap up
There are many options for a newbie to learn programming. As well as there are hundreds of code languages to start with. But the ones reviewed here are the world’s top-rated technologies and they remain this way for years. So, I think this will help you and you will find a way to contribute to this industry.